Could a car's entertainment system provide a route to its brakes?
In 2015, security researchers demonstrated that possibility in a Jeep Cherokee. They remotely accessed its infotainment system, which runs in-car entertainment, and interfered with driving functions.
Fiat Chrysler subsequently announced a recall covering approximately 1.4 million vehicles across the US to install a software update that fixed the flaw.
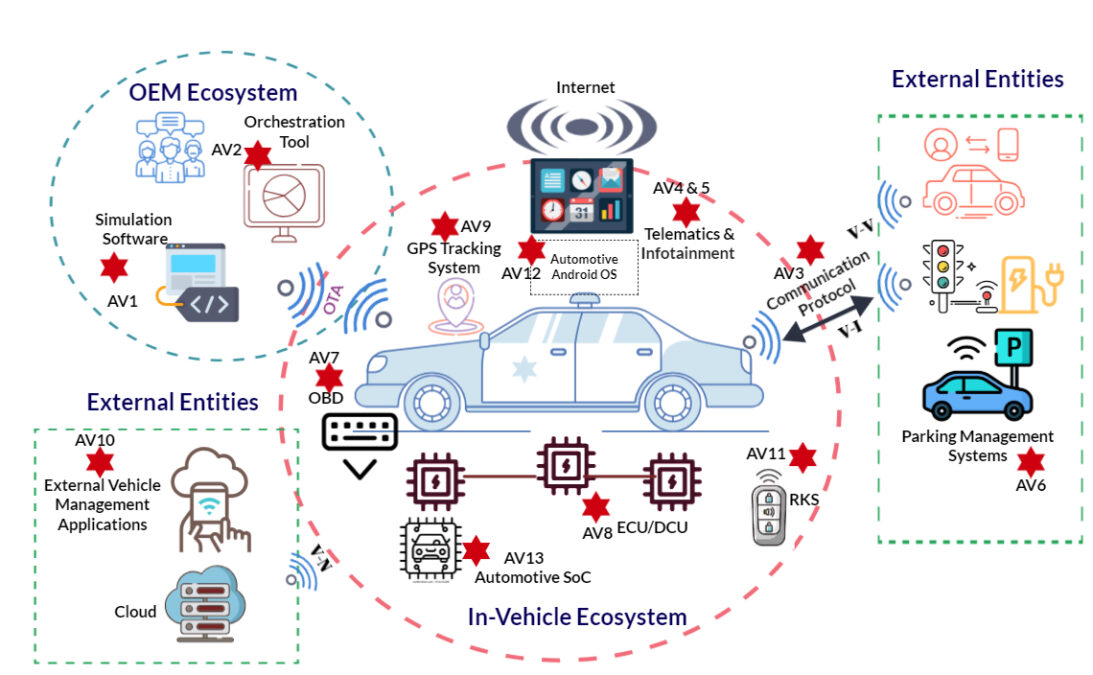
That attack targeted a system built into the car. A recent study examines a wider network, including the apps and online services connected to vehicles.
Researchers at Sweden's University of Gothenburg and Chalmers University of Technology analyzed 413 previously reported automotive software vulnerabilities. External applications accounted for the largest share, at 36.2 percent.
Their study, published in Software Quality Journal, also identified a shift toward externally connected software compared with earlier research.